Microsoft Security Specialist
Security partnership with Cloud Security specialization
SOC Services extend MDR with the deeper analytics, threat hunting and forensic capability that comes with running a true 24/7 Security Operations Centre. We pull logs from everything — identity, firewalls, endpoints, servers, cloud — correlate them in one place, and proactively look for the things that don’t trip a single rule but tell a clear story when joined up.
It’s the difference between having a bouncer at the club and having a full security operation, with cameras, intel, and a team that’s looking for trouble before it starts.
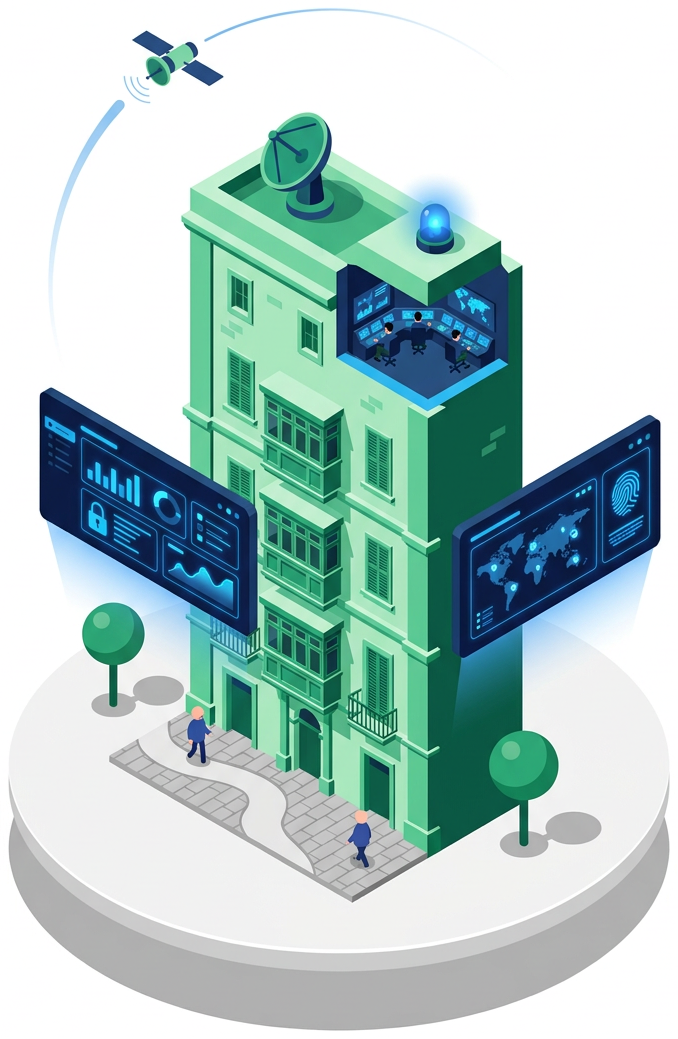
Most companies can’t justify the cost of staffing, training and retaining a 24/7 SOC team — let alone the SIEM, SOAR and threat intelligence subscriptions that come with it. With ICT Solutions, you get all of it as a service: alert fatigue eliminated, visibility complete, and the risk taken off your shoulders.
Centralised Visibility
Incident Forensics
Proactive Threat Hunting
Threat Intelligence
24/7 Coverage
Our SOC runs on Microsoft Sentinel and Fortinet — the same platforms our clients use, integrated tightly. That means faster onboarding, deeper visibility, and a smoother handoff between detection, response and remediation.
Security partnership with Cloud Security specialization

Integrated Fortinet security operations expertise
Round-the-clock response covering 2,000+ seats
Monthly, from 300–500 priority security alerts
A few of the questions we get asked most often.
SOC (Security Operations Centre) services provide a dedicated team and facility that monitors an organisation’s IT environment for security threats 24/7. The SOC collects and analyses signals across systems, detects suspicious activity, and coordinates response—acting as the central nerve centre for an organisation’s cyber defence.
ICT Solutions operates a Security Operations Centre staffed by security analysts and built on Microsoft Sentinel SIEM and Fortinet technologies. ICT aggregates logs and telemetry across your environment, monitors around the clock, investigates incidents, and coordinates response – offering local businesses a shared or dedicated SOC without the cost of building one in-house.
Building an in-house SOC is out of reach for most Maltese organisations given cost and the local security-skills shortage. A local SOC partner delivers continuous monitoring and fast response on-island, helping Maltese finance, iGaming, and public-sector bodies meet NIS2 and DORA monitoring obligations affordably.
Our SOC-as-a-Service Starter Guide covers what’s actually inside a real SOC — and how to evaluate providers honestly.
We are excited for our work and how it positively impacts clients.
Otech strengthened its day-to-day technology operations with managed IT and security support designed around the needs of its growing business.
Arringo adopted a proactive managed security approach to strengthen protection, visibility and ongoing support across its technology environment.
Andaria built a secure, scalable cloud foundation that supports reliable operations and gives the business room to grow.
Mizzi Organisation strengthened cyber resilience across its diverse operations through a coordinated managed security service and continuous specialist support.
AX Group modernised its network with Fortinet technology, creating a more secure and consistent foundation for connectivity across the organisation.
A market-leading iGaming company strengthened its cyber resilience with a security programme designed for a fast-moving, digitally driven environment.

© 2026 ICT Solutions. All Rights Reserved.