Microsoft Security Partner
Defender and Sentinel security expertise
No security stack is perfect. People click links, devices get stolen, credentials leak, zero-days happen. The question isn’t whether something will get through — it’s whether anyone will see it before damage is done.
Managed Detection & Response is the floor of every serious security programme. It makes sure that when an attacker gets a foothold, our team sees it, contains it, and removes it — before it becomes the breach you’d rather not explain.
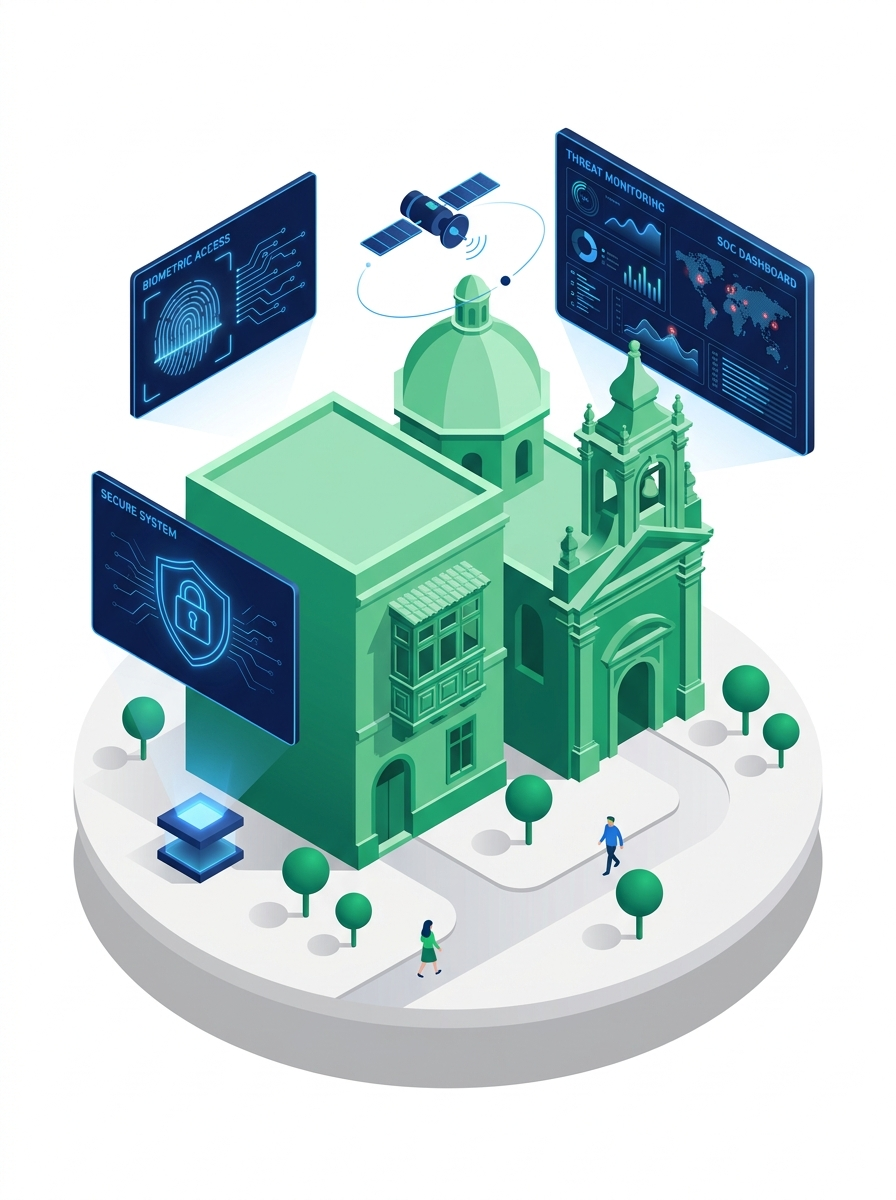
MDR isn’t about more alerts. It’s about the right alerts, validated by analysts, and acted on in time. We run it as a true managed service — your team gets fewer interruptions, and the incidents that matter actually get handled.
Continuous Monitoring
Incident Response
Threat Investigation
Reporting & Communication
Compliance Alignment
Most clients come to MDR for peace of mind. They stay because of the evidence — clean detection coverage, validated incident response, and quarterly proof of value that supports both their security goals and their regulatory obligations.
Defender and Sentinel security expertise

Deep Fortinet detection and response capability
Critical response covering 2,000+ seats
Every month by the security operations team
A few of the questions we get asked most often.
Managed Detection and Response (MDR) is a fully managed service that continuously monitors an organisation’s systems for cyber threats and responds to them in real time. Combining security tooling with expert analysts, MDR detects, investigates, and contains attacks – like ransomware or intrusions – that automated tools alone would miss, around the clock.
ICT Solutions delivers MDR through its Security Operations Centre, using Microsoft Sentinel, EntraID and Defender alongside Fortinet and other telemetry to detect and investigate threats 24/7. ICT’s analysts triage alerts, hunt for threats, and respond – isolating affected systems and guiding remediation – giving clients enterprise-grade detection and response without building the capability themselves.
Most Maltese businesses can’t staff a 24/7 security team, yet threats and NIS2/DORA obligations don’t pause. MDR gives local firms continuous, expert protection with rapid on-island response, helping regulated sectors like finance and iGaming meet monitoring and incident-response requirements without hiring scarce specialists.
Our MDR: A Getting Started Guide explains how MDR fits into a wider security stack — and how to evaluate providers.
We are excited for our work and how it positively impacts clients.
Otech strengthened its day-to-day technology operations with managed IT and security support designed around the needs of its growing business.
Arringo adopted a proactive managed security approach to strengthen protection, visibility and ongoing support across its technology environment.
Andaria built a secure, scalable cloud foundation that supports reliable operations and gives the business room to grow.
Mizzi Organisation strengthened cyber resilience across its diverse operations through a coordinated managed security service and continuous specialist support.
AX Group modernised its network with Fortinet technology, creating a more secure and consistent foundation for connectivity across the organisation.
A market-leading iGaming company strengthened its cyber resilience with a security programme designed for a fast-moving, digitally driven environment.

© 2026 ICT Solutions. All Rights Reserved.