AttackIQ Partner
Adversarial exposure-validation platform
Don’t take our word for it. Test your defences with the same techniques real attackers use.
Traditional pen testing has its place — but for most organisations, it tells you what a small two-person team in a basement managed to find in a few days, once a year. Real-world attacks come from the FSB, North Korean operators, well-funded ransomware groups, and they use techniques those small teams would never replicate.
Adversarial Attack Simulation takes the actual techniques those threat actors use, removes the dangerous payload, and lets them loose in a controlled way against your environment. The verdict is honest, often uncomfortable, and exactly what you need before someone else does it for real.
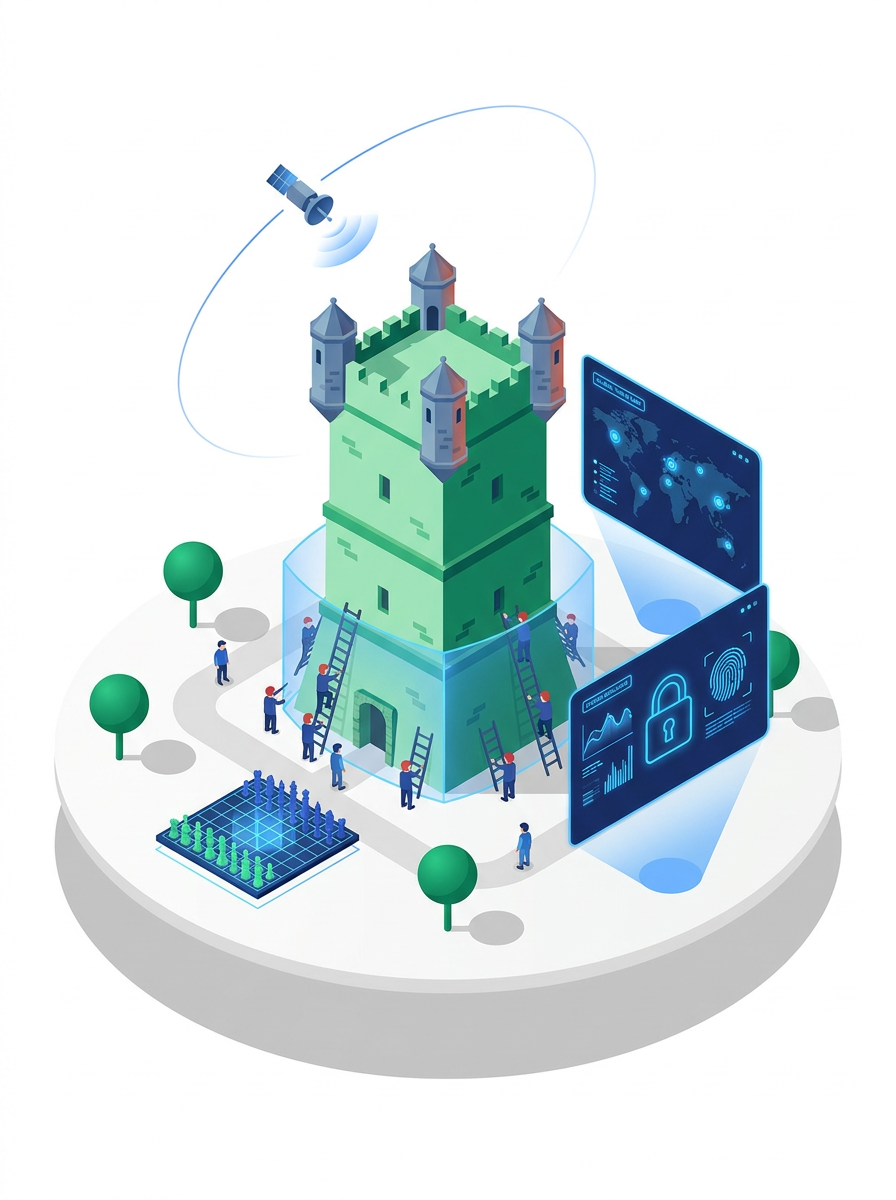
Our service is built on a leading attack simulation platform and run by our security team. We can test your systems, your processes, and your people’s response — and we do it on a continuous basis so the picture stays current.
System Testing
Continuous Validation
Reporting & Remediation
Process & Team Testing
Threat Coverage
CTEM Integration
We run adversarial simulation against our own environment every six months. Even with very good security, the reports always surface something worth fixing. That’s the point — uncomfortable truths are useful, and a lot cheaper than the alternative.
Adversarial exposure-validation platform
Security-control and detection expertise
We run adversarial simulation against ourselves
Continuous improvement within an audited ISMS
A few of the questions we get asked most often.
Adversarial attack simulation – including penetration testing and red teaming – is a controlled exercise where security experts safely mimic real cyber-attacks against an organisation. It reveals how well defences, systems, and people would withstand a genuine attack, uncovering vulnerabilities before criminals do so they can be fixed.
ICT Solutions runs controlled tests and attack simulations against your networks, applications, and users, using recognised methodologies and attacks used by real hackers. ICT scopes the engagement, safely exploits weaknesses, and delivers a prioritised report with clear remediation guidance – then helps close the gaps, turning findings into a stronger security posture.
Regular testing is increasingly expected – and in some cases required – of Maltese regulated entities under frameworks like DORA. For local finance and iGaming operators, attack simulation provides both compliance evidence and genuine assurance, delivered by a local partner who understands the Maltese threat and regulatory landscape.
Our Adversarial Simulation Starter Guide explains how this differs from pen testing, what to expect, and how to measure progress.
We are excited for our work and how it positively impacts clients.
Otech strengthened its day-to-day technology operations with managed IT and security support designed around the needs of its growing business.
Arringo adopted a proactive managed security approach to strengthen protection, visibility and ongoing support across its technology environment.
Andaria built a secure, scalable cloud foundation that supports reliable operations and gives the business room to grow.
Mizzi Organisation strengthened cyber resilience across its diverse operations through a coordinated managed security service and continuous specialist support.
AX Group modernised its network with Fortinet technology, creating a more secure and consistent foundation for connectivity across the organisation.
A market-leading iGaming company strengthened its cyber resilience with a security programme designed for a fast-moving, digitally driven environment.

© 2026 ICT Solutions. All Rights Reserved.